Data Transfer Assessment
by Formiti's Global DPO Team
A structured place to review international personal data transfers. Record what moves, who receives it and where it is accessed; document the applicable transfer mechanism, destination context, supplementary measures and the decision reached by your privacy and legal teams.
Who uses this module?
DPOs, Privacy Counsel, Legal Teams, Vendor Risk Managers and business owners responsible for cross-border processing.
What governance problem does it solve?
A contract alone does not explain the complete transfer. The people assessing it also need to understand the underlying processing, remote access, onward transfers and the safeguards in practice. Bringing the facts, rationale and review ownership together makes it easier to revisit the decision when a supplier or data flow changes.
What are the key workflows?
- Identify the exporting and receiving entities, processing purpose, data categories, destinations and any remote access or onward transfers
- Record the transfer mechanism and supporting documents relevant to each data flow
- Assess the destination context and practical risks with input from legal, privacy and technical reviewers
- Document supplementary measures and outstanding actions alongside the transfer decision
- Assign an owner, record the approval rationale and set a review point when facts or safeguards change
Identify the exporting and receiving entities, processing purpose, data categories, destinations and any remote access or onward transfers
Record the transfer mechanism and supporting documents relevant to each data flow
Assess the destination context and practical risks with input from legal, privacy and technical reviewers
Document supplementary measures and outstanding actions alongside the transfer decision
Assign an owner, record the approval rationale and set a review point when facts or safeguards change
What evidence and reporting does it produce?
Built-in outputs for accountability and regulatory readiness
Transfer scope and destination recorded with the underlying processing activity
Mechanism, contracts and supporting evidence alongside the assessment
Risk rationale, safeguards, reviewers and decision history
Follow-up actions and reassessment triggers for changes to suppliers, access or hosting
How does it connect to other Privacy360 modules?
- ROPA Records provide the processing context, data categories and recipient details for a transfer review
- Privacy Assessments provide the wider assessment workspace for transfer, DPIA and related privacy questions
- Vendor Assessments add due diligence and review evidence for suppliers receiving or accessing data
- Processor Records connect the recipient and sub-processor chain to contract and oversight records
What are some example use cases?
A procurement team reviews a new analytics supplier with support access from another country and records both the transfer mechanism and the practical access controls before approval.
A group privacy team revisits an existing transfer after a processor changes its hosting location or adds a sub-processor.
A DPO brings together the processing record, supplier due diligence and legal analysis for an international HR data flow so the rationale can be reviewed later.
Frequently asked questions
What is a data transfer assessment?
It is a documented review of a cross-border personal data flow: who sends and receives the data, where it can be accessed, the transfer mechanism, relevant destination risks and the safeguards needed before a decision is made.
Is a signed contract enough to complete a transfer review?
Not on its own. A review should also consider the actual data flow, the destination context, access and onward transfers, and whether the agreed safeguards work in practice. Legal advice may be needed for the applicable jurisdiction.
How does this connect to ROPA and vendor assessments?
The processing record supplies the purpose, data categories and recipients; vendor due diligence supplies information about the supplier and its controls. A transfer assessment records the decision about that cross-border flow and its safeguards.
When should a transfer assessment be reviewed again?
Review it when relevant facts change, such as the destination, access arrangements, sub-processors, categories of data or safeguards. The appropriate review interval also depends on the risks of the transfer.
Related modules
ROPA Records
Maintain records of processing activities with clear ownership, data mapping, review controls and AI Processor disclosure — and let the record automatically open and pre-fill the DPIA, LIA, transfer and AI assessments it triggers.
Privacy Assessments
Run global privacy gap assessments, DPIAs, LIAs, transfer reviews and vendor assessments against 150+ controls — with structured rationale, evidence and AI-assisted review.
Vendor Assessments
Score third parties against privacy and security criteria, rate portfolio risk, and hold vendors to reassessment cycles rather than one-off checks.
Processor Records
Maintain structured processor and sub-processor records with contract status, ownership and review evidence.
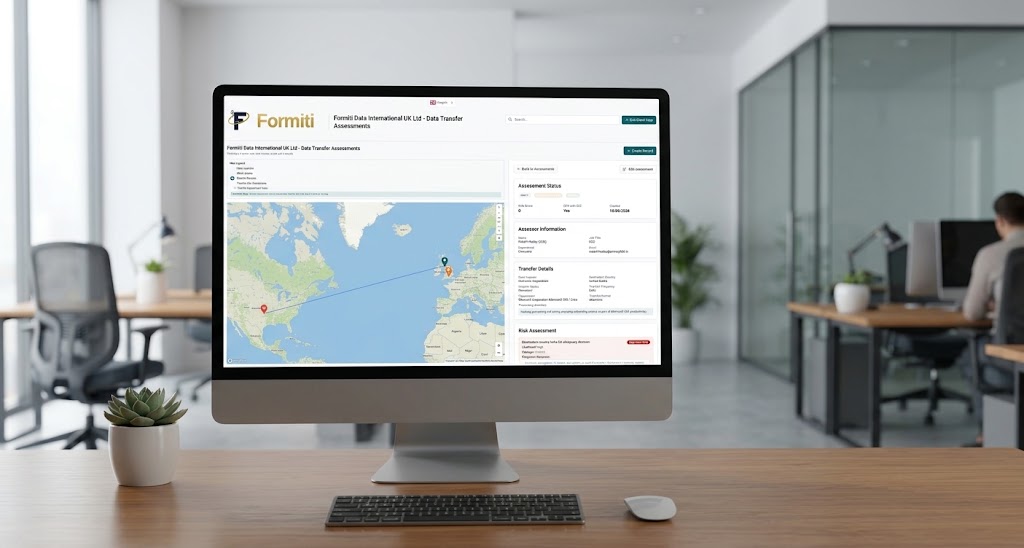
Cross-border transfers in practice
International data flows need more than a signed agreement. Map access and onward transfers, assess the destination, document the safeguards and keep the decision under review.
Read the cross-border transfer guideData Transfer Assessment guides
Practical articles from Formiti's Global DPO team on running this work well.